The corporate dream is seductively simple – build an autonomous AI agent once, release it everywhere, and watch it scale while the humans vanish to an off-site to discuss “strategy” over coffee that tastes faintly of procurement. The agent doesn’t need sleep, visas or one of those motivational breakfasts where the croissants are expected to improve morale. It can negotiate, screen, recommend, classify and transact across borders before legal has finished clearing its throat and saying, “There is, however, one small concern.” There is always one small concern. It’s almost never small.
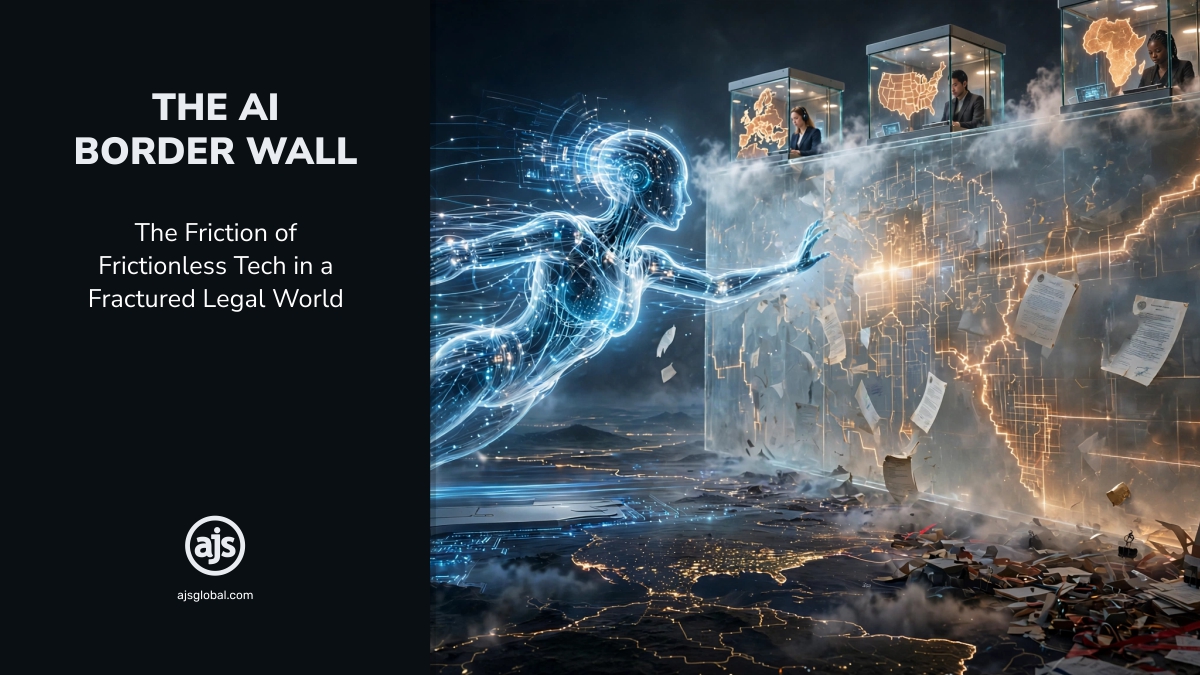
Borders, inconveniently, haven’t read the product roadmap. AI may be frictionless, but the law is gloriously, stubbornly territorial. It comes with local definitions, enforcement cultures, constitutional values, data-transfer rules and the occasional regulator who regards “the model did it” as less of a defence than a useful opening admission.
Borders are basically territorial Bengal cats – magnificent, expensive and deeply offended when another cat so much as puts one paw across the invisible line, they’ve drawn around the sofa, the garden and, apparently, international data flows.
That collision is the friction economy – borderless automation meeting institutions that still have jurisdictions, filing deadlines and long memories. The more companies automate globally, the more valuable good human judgement becomes. Counter-intuitive? Only until a board discovers that its “global solution” has 14 local exceptions, three nervous directors and one slide nobody now admits approving. Lawyers aren’t valuable here because they enjoy obstructing progress – although, admittedly, you do own excellent stationery. You’re valuable because no autonomous system can yet turn conflicting laws, political risk and commercial appetite into one defensible decision.
Global AI Regulation Is Fragmenting Faster Than Companies Can Centralise
The problem isn’t a lack of regulation. Quite the opposite – everyone is regulating AI, often differently and occasionally as though nobody else received the calendar invitation. The European Commission began enforcing important AI Act rules from 2 August 2026, including transparency duties for certain AI interactions and synthetic content. Depending on the breach, transparency-related fines can reach €15 million or 3% of global annual turnover. Nobody calls it an ethics workshop after the invoice arrives.
The EU framework is risk-based and increasingly harmonised. It’s also had to adjust its own timetable. Regulation (EU) 2026/1744 amended the AI Act after delays in standards and national conformity-assessment arrangements made compliance heavier than expected. Businesses were building against the rulebook while somebody was still editing the rulebook. Agile regulation met agile development. There were stand-ups. Nobody stood up any faster.
Across the Atlantic, there still isn’t one comprehensive US federal AI law. Instead, there’s the familiar American arrangement – a fast-moving patchwork of state, municipal and sector-specific requirements. California, Texas, Illinois, New York City, Utah and Colorado don’t share one tidy compliance personality. Their rules cover different combinations of automated decision-making, frontier-model transparency, discrimination, hiring, disclosure and consumer protection. On a slide, “deploy nationally” takes two words. In practice, it means several control environments, several legal opinions and somebody trying not to panic while explaining that procurement has already promised Tuesday.
AI Sovereignty Turns One Global Product into Several Local Legal Entities
Europe is only one wall in the maze. China’s Interim Measures for Generative AI Services regulate public-facing services within China alongside cybersecurity, data-security and personal-information rules. Providers can face training-data, content, labelling, security-assessment and algorithm-filing duties that don’t mirror the EU’s architecture. The agent sees an API call. Sovereign law sees the jurisdiction, purpose, data category, affected person and transfer route – then asks who approved all of it. If everyone is unlucky, that is the beginning of a very long week.
Southeast Asia offers a different model. The ASEAN Guide on AI Governance and Ethics is practical and voluntary, encouraging alignment and interoperability across jurisdictions. It emphasises transparency, fairness, security, human-centricity, privacy, accountability and risk-calibrated human involvement. Sensible, all of it. But it isn’t a magic passport. Voluntary regional guidance still has to coexist with member-state laws, sector rules and the thoroughly local habits of enforcement. Regulators, like families, may share values without agreeing on how anything should actually be done.
Africa’s direction matters just as much, and its context isn’t a footnote to somebody else’s framework. The African Union’s Continental Artificial Intelligence Strategy, endorsed in July 2024, calls for Africa-centric, ethical and inclusive AI, stronger capabilities, risk management, investment and cooperation. It points towards continental alignment, but domestication remains national. Shared direction isn’t identical local law. Confuse the two and the elegant regional map in the strategy deck eventually becomes a much less elegant boardroom story.
South African AI Compliance Starts with Existing Law, Not a Future AI Act
South African boards may be tempted to wait for a neat, dedicated AI Act to descend from the legislative heavens wearing a lanyard and carrying a compliance checklist. Don’t. AI deployments already sit inside existing obligations: the Protection of Personal Information Act, consumer law, employment law, equality protections, cybersecurity duties, intellectual-property rules, sector regulation and directors’ governance responsibilities. The absence of a single AI statute isn’t the absence of liability. It’s liability without a convenient name badge.
Government did, to be fair, attempt to supply the name badge with its 2026 draft national AI policy – only to withdraw it after the references turned out to include AI-generated hallucinations. It was the regulatory equivalent of appointing a cat to chair the committee on unattended tuna, then acting astonished when the minutes simply read, “Meow, source unavailable.” A policy meant to demand vigilant human oversight had apparently left its own human unsupervised near the “generate” button.
A globally centralised model creates awkward data-sovereignty questions almost immediately. Where was the information collected? Where was it inferred, enriched, stored, reviewed and reused? Is the output merely a recommendation, or does everyone treat it as a decision until litigation points out the distinction? When a vendor’s model, a local deployer’s workflow and an employee’s click combine to cause harm, the architecture diagram offers cheerful arrows. The regulator would prefer a name.
That’s why “we use the same stack everywhere” isn’t governance. It’s administrative neatness wearing a steering-committee lanyard. Localisation may require different data sets, notices, escalation thresholds, retention periods, human-review points, contracting terms and even disabled functionality. Standardisation is still useful, but only as a controlled baseline from which necessary differences are managed. Pretending those differences don’t exist merely gives the eventual enforcement letter better material – and, possibly, headings.
Why Autonomous AI Agents Can’t Reconcile Conflicting Global Laws
AI can compare legislation, flag obligations and produce an impressive memo before a junior associate has found the correct charging cable. That’s genuinely useful. But it can’t reliably decide which conflict the business should carry, which market concession is politically tolerable, or when strict compliance in one jurisdiction quietly creates exposure in another. Those aren’t retrieval problems. They’re judgement calls involving law, diplomacy, evidence, commercial priorities and institutional nerve – the untidy things that refuse to sit politely in a dropdown menu. Unfortunately.
Take incident reporting. The OECD’s common reporting framework for AI incidents uses 29 criteria to support interoperability while allowing domestic adaptation. It’s useful precisely because the underlying problem remains messy. Jurisdictions can define incidents, materiality, responsible actors and reporting deadlines differently. An agent can fill in boxes. It can’t decide how to preserve legal privilege, manage competing notifications or handle the moment one regulator learns what another was told.
- Remember interoperability?
That’s the grand technical ideal of getting different systems and jurisdictions to speak to one another without somebody shouting, “That’s not what our form means,” and attaching a 47-page guidance note in reply.
Boards shouldn’t confuse technical sophistication with legal reliability either. The Stanford 2026 AI Index reports that organisational AI adoption reached 88% in 2025, while generative AI was used in at least one business function at 70% of surveyed organisations. It also found that AI-agent deployment remained in the single digits across almost every business function. The economics are compelling, so adoption is moving quickly. Governance is keeping its usual schedule, though – after the pilot, before the inquiry and, ideally, once another company has kindly supplied the cautionary tale.
Human Legal Judgement Is the Premium Product in the Friction Economy
Human judgement is often called the bottleneck, usually by someone selling software that removes bottlenecks. It’s a clever frame, but a poor description of the economics. In a fragmented regulatory world, judgement is the premium layer – the scarce ability to interpret ambiguity, weigh competing sovereign demands, read enforcement temperament and tell a board which risks are survivable – and which will look frankly deranged in the minutes 18 months later.
The valuable lawyer won’t manually reread every rule whenever an agent crosses a border. That isn’t judgement; it’s expensive scrolling. Technology should maintain inventories, map controls, monitor change, retain evidence and surface conflicts. Counsel earns the premium by resolving what automation exposes – whether a use case should be redesigned, ring-fenced, delayed, locally hosted, contractually reallocated or abandoned before optimism retains litigation counsel of its own.
This changes the law-firm profit conversation too. If firms keep charging premium rates for work machines can do, clients will eventually notice. Some already own calculators. The defensible premium lies in accountable interpretation, cross-border orchestration and advice that can survive regulatory, judicial and shareholder scrutiny. Less document tourism and more legal statecraft. And, with luck, fewer partners explaining that copying a clause into 12 jurisdictions constitutes innovation.
What Boards Must Demand Before Scaling AI Across Borders
Start with a jurisdiction-by-jurisdiction AI use-case register, not a decorative “AI policy” last opened during onboarding. Record the system, its purpose, the people affected, data flows, vendor chain, legal basis, risk classification, decisions influenced and the executive who owns it. If nobody owns it, that isn’t agility. It’s an orphan with processing power and access to customer data.
Then agree a global minimum control set and document the local overlays. Every exception needs an owner, a rationale, a review date and evidence. If the answer is “the vendor handles compliance”, ask the vendor for an indemnity broad enough to match that confidence. The conversation usually becomes more nuanced. Sometimes it even develops punctuation.
Decide who has human authority before deployment. Who can stop the system, override an output, approve a new market, notify a regulator or reject a commercially attractive use case? “Legal was consulted” isn’t governance when legal’s advice appears in the minutes immediately before the business does the opposite. That’s not consultation. It’s foreshadowing.
Finally, test the operating model, not only the model. Run cross-border scenarios involving data transfers, discrimination, incorrect disclosures, vendor failure and contradictory reporting duties. Ask who gets called at 02:00, what evidence they can retrieve and whether the person with authority is actually awake. A system that works perfectly until something goes wrong isn’t resilient. It’s a brochure with electricity.
Can Borderless AI Scale Survive Local Compliance Laws?
True autonomous global scale may be technically possible. Legally uniform scale probably isn’t. Sovereignty isn’t a software defect awaiting a patch; it’s how jurisdictions express different values around privacy, speech, discrimination, security, labour and national interest. Interoperability can reduce friction, but it can’t abolish politics – software has tried many ambitious things, but that would be showing off. The grown-up ambition isn’t one agent behaving identically everywhere. It’s one enterprise knowing exactly when, why and how that agent must behave differently.
Legal judgement, then, isn’t overhead. It’s infrastructure. Companies that bring counsel into architecture, procurement and market-entry decisions will usually move faster because they know where the brakes are and which one’s work. Those that bolt legal on afterwards may also move quickly – generally towards disclosure obligations, emergency board meetings and invoices containing the words “urgent regulatory response”. Speed, as ever, depends on the direction of travel.
~
AJS helps legal teams turn scattered obligations into working controls, visible ownership and evidence people can actually find. If your AI expansion crosses jurisdictions, don’t hand the board another static policy and call it governance. Build the legal operating layer before rollout – what’s deployed, where the risk sits, who made the call and what supports it. Because sooner or later a regulator will ask the irritatingly reasonable question: “Why?”
And honestly, it’s better to have an answer than a workshop.
(Sources used and to whom we owe thanks: EUR-Lex, Regulation (EU) 2024/1689 (Artificial Intelligence Act); EUR-Lex, Regulation (EU) 2026/1744; European Commission, Commission starts enforcing AI Act rules and new transparency requirements; European Commission, Safer and more transparent AI; AI Compliance Atlas, US State AI Regulation Overview; China Law Translate, Interim Measures for the Management of Generative Artificial Intelligence Services; ASEAN, Guide on AI Governance and Ethics; African Union, Continental Artificial Intelligence Strategy; South African Government, Protection of Personal Information Act 4 of 2013; Reuters, South Africa withdraws AI policy due to fake AI-generated sources; OECD, Towards a common reporting framework for AI incidents; and Stanford Institute for Human-Centered Artificial Intelligence, 2026 AI Index Report).